

Key takeaways
- Fraud can originate at any level. Employees, managers and executives may exploit weaknesses in controls or override existing safeguards.
- The financial impact can be substantial. The ACFE’s 2026 global study recorded a median loss of US$104,000 per case. Its separate estimate that organisations lose 5% of annual revenue to fraud is based on practitioners’ assessments, not a measured average across the cases studied.
- Warning signs need verification. Unusual transactions, missing documents and unexplained changes to supplier bank details warrant checks; they do not establish fraud.
- Reporting channels matter. Tips detected 43% of cases in the ACFE study, including information from employees and external parties.
- Prevention starts with practical controls. Separate payment responsibilities, restrict access, review exceptions and train staff.
- Legal requirements vary. EU whistleblowing rules provide a common baseline, while national law determines many reporting and investigation obligations.
Internal fraud in businesses is a discreet but costly risk. It originates from within, in an increasingly digital working environment. Understanding, detecting and preventing it is becoming a key management reflex.
What is internal fraud?
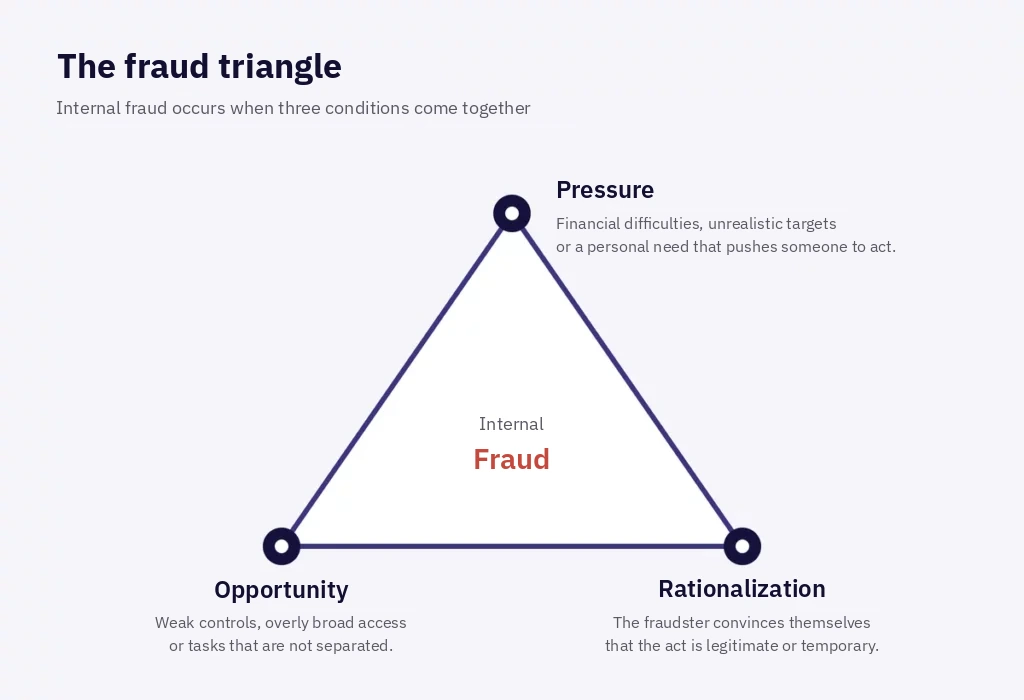
Internal fraud occurs when an employee, manager or executive deceives their organization for personal gain. Here is a simple definition to remember. Researchers summarize its causes through the “fraud triangle”: pressure, opportunity and rationalization. Addressing these three factors, at the heart of any compliance implementation, significantly reduces the risk. This phenomenon affects businesses of all sizes, in France and elsewhere.
The fraud triangle is a risk assessment framework, not a test for identifying individual offenders. Businesses can reduce opportunities through internal controls and address rationalisation through clear expectations, consistent accountability and ethical leadership.
Internal fraud versus external fraud
| Criterion | Internal fraud | External fraud |
|---|---|---|
| Perpetrator | Employee, manager or executive | Customer, supplier, impersonator or other third party |
| Examples | Asset theft, fictitious expenses, payroll manipulation | Phishing, payment diversion, fraudulent supplier invoices |
| Main controls | Segregation of duties, access controls, oversight and reporting channels | Cybersecurity, independent verification and third-party checks |
Common types of internal fraud in 2026
Certain methods occur repeatedly. Here are the main ones:
- Asset misappropriation: theft of cash, inventory or equipment.
- Corruption and conflicts of interest.
- Financial statement fraud, the most costly form of fraud.
- Expense and payroll fraud.
- Payment fraud committed or facilitated by an employee. Fraudulent payment orders generally fall under external fraud, unless they involve internal collusion or the deliberate circumvention of controls.
Sophisticated financial schemes, explored in our analysis of “the biggest investment frauds“, coexist with much simpler schemes. Our lessons learned from corporate fraud remind us that no industry is truly immune.
Why internal fraud is a major business risk
Financial losses and reputational damage
The ACFE’s 2026 Report to the Nations examines 2,402 investigated cases across 143 countries and territories. A typical scheme lasted 12 months before detection. These are international findings from investigated cases, not estimates of fraud prevalence in EU businesses.
Beyond the immediate loss, an incident can trigger investigation costs, operational disruption, disputes and loss of trust among employees, lenders and commercial partners. Seniority can increase exposure when an individual has extensive approval powers or the ability to override controls.
Governance and compliance weaknesses
Fraud can expose missing controls, ineffective supervision or deliberate circumvention of established procedures. Updating policies alone will not resolve a weakness if the same person can still create a supplier, approve an invoice and release the payment.
Effective corporate governance requires clear ownership of controls, meaningful challenge and a route for escalating concerns about senior management.
Risks to EU grants and institutional funding
Ineligible expenditure, serious irregularities or fraud can lead to payment suspension, grant reductions or recovery of funds already paid. The outcome depends on the programme, the facts and the applicable funding agreement. The European Commission explains these mechanisms in its guidance on protecting the EU budget.
For funding recipients, reliable procurement records, cost evidence and approval trails help protect both current projects and future funding relationships.
How to detect internal fraud: warning signs and checks
Accounting and payment anomalies
Financial red flags include duplicate invoices, unusual journal entries, unsupported expenses, unexplained supplier changes and transactions repeatedly falling just below approval thresholds.
Context matters. Frequent payments to a regular supplier may be entirely normal; payments without a valid contract, evidence of delivery or independent approval deserve closer examination.
Behavioural warning signs
Persistent resistance to independent review, refusal to delegate sensitive tasks or unusually close supplier relationships may justify checking the underlying controls. Personal circumstances, lifestyle or reluctance to take leave must never be treated as proof.
The ACFE reports that 84% of perpetrators in its 2026 study displayed at least one behavioural red flag. This retrospective finding does not mean that people displaying such behaviours are likely to commit fraud. Source: ACFE 2026 press release.
How to check a red flag without jumping to conclusions
| Warning sign | Possible explanation | Initial check | Safeguard |
|---|---|---|---|
| Unusual payment | Error, supplier fraud or collusion | Compare the contract, invoice, delivery evidence and approvals | Establish the facts before drawing conclusions |
| Missing supporting documents | Process failure or fictitious expenditure | Review accounting records and transaction history | Preserve original records and metadata |
| Changed supplier bank details | Legitimate update or payment diversion | Call a verified contact using an independently held number | Pause the affected payment where justified |
| Persistent refusal to delegate | Operational dependency or concealed control override | Review access rights and approval responsibilities | Focus on process evidence rather than personal profiling |
Internal control tools and systems for detecting fraud
Detection relies above all on listening. Internal reports uncover 43% of fraud cases, far ahead of audits, according to the ACFE. A confidential reporting hotline can even halve the duration of a fraud scheme. Digital data analysis tools, sometimes powered by artificial intelligence, help identify anomalies.
Screening business partners through proportionate due diligence completes this framework. A properly handled report, submitted through a protected corporate whistleblowing system, can make all the difference.
Vérifier ses partenaires, par une due diligence proportionnée, complète ce dispositif. Un signalement bien traité, via un lanceur d’alerte en entreprise protégé, change tout.
Is your whistleblowing channel compliant?
How to prevent internal fraud
Strengthen internal controls
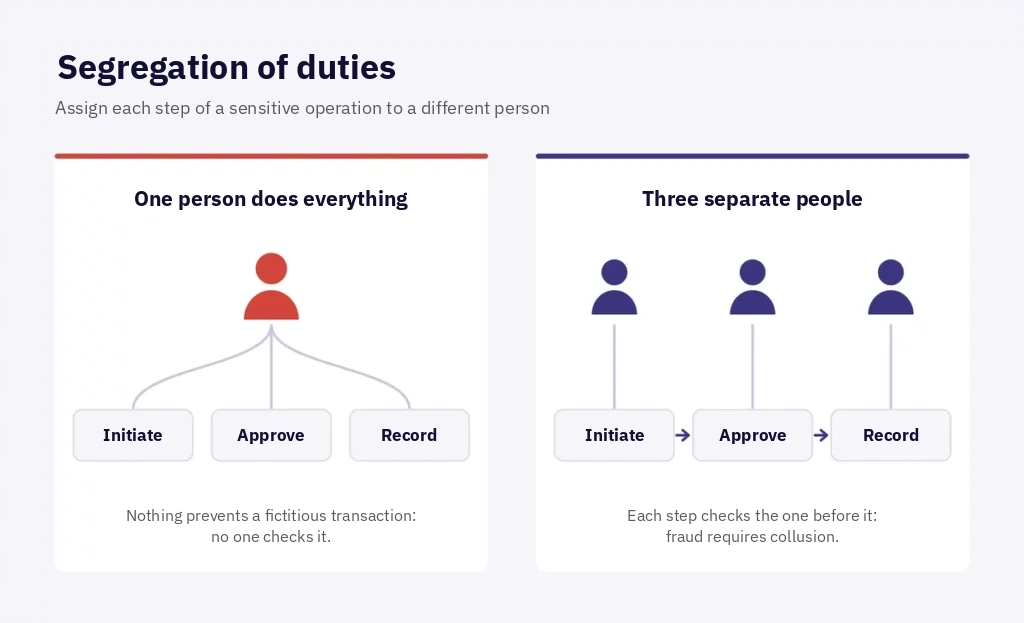
The best defence remains a well-structured organisation. Segregation of duties, strict management of IT access and traceability of sensitive operations limit opportunities for fraud. Assigning access rights according to each role further strengthens this foundation.
Train employees and managers
Well-informed teams are better equipped to spot misconduct. The ACFE observes that reports are twice as frequent following anti-fraud training. Clear communication and regular awareness-raising gradually foster an ethical culture.
The role of statutory auditors and internal audit
Statutory auditors and internal audit provide an independent perspective. Their regular checks deter fraudsters and help detect anomalies and incidents. They also strengthen the credibility of financial statements among third parties.
Internal audit assesses risk management processes and can identify certain anomalies. When appointed, the statutory auditor seeks, in particular, to obtain reasonable assurance that the financial statements are free from material misstatement, including misstatements resulting from fraud. However, their involvement does not guarantee the detection of all fraud.
Integrating fraud risk into overall risk management
Fraud is not just a financial issue. Incorporating it into overall risk management, alongside cybersecurity, technological and legal challenges, ensures a consistent approach. However, no solution offers an absolute guarantee.
Regulatory framework and legal obligations relating to internal fraud
Sapin II Law and anti-corruption measures
The 2016 Sapin II Law requires large companies to implement an anti-corruption programme. The threshold is 500 employees and €100 million in annual revenue. The French Anti-Corruption Agency (AFA) oversees its implementation. Article 17 of the Sapin II Law requires companies with at least 500 employees and annual revenue exceeding €100 million to implement measures to prevent and detect corruption and influence peddling. Specific rules also apply to groups whose parent company is headquartered in France. This anti-corruption framework can help manage certain fraud risks, but its scope does not cover all forms of internal fraud indiscriminately.
Protection of whistleblowers in businesses
Since the 2022 Waserman Law, all private legal entities employing at least 50 people must provide a secure reporting channel and procedure. Whistleblower protection is not limited to employees: it may also extend to individuals covered by the law who report or disclose information in good faith and without direct financial compensation.
Reporting obligations and management responsibilities
Senior management retains ultimate responsibility. It must organise a proportionate response: preserve evidence, protect the individuals concerned, conduct the necessary investigations and determine, with its advisers, the appropriate disciplinary, civil, criminal or regulatory measures. Notification to an authority is only mandatory in cases provided for by applicable legislation or sector-specific regulations.
Examples of internal fraud in European SMEs and mid-sized companies
Small organisations are not immune to internal fraud; quite the opposite. According to the ACFE’s 2026 global study, businesses with fewer than 100 employees record the highest median loss of all categories studied: $126,000 per case.
Several factors may explain this. Smaller teams make segregation of duties more difficult: the same person may be responsible for initiating, approving and recording a transaction. Controls are also less formalised, and the trust placed in long-standing employees sometimes takes the place of proper verification procedures. In a challenging economic climate, a loss of this magnitude can have a lasting impact on an SME’s cash flow. Company size is therefore no guarantee of protection.
- Note : ACFE data is based on an international sample. It provides insight into observed trends but does not specifically describe the European SME and mid-sized business landscape.
Two common mistakes when handling an internal fraud case
- Reacting hastily, without solid evidence. Acting too quickly can lead to procedural errors, unusable evidence and litigation.
- Confusing suspicion with proven misconduct. A suspicion, even a well-founded one, is not proof. Wrongly accusing someone can harm an innocent employee and expose the company to liability.
In both cases, discretion and a methodical approach must take priority: secure the evidence, limit the circle of people informed, then conduct a structured investigation before making any decisions.
Best practices for securing sensitive processes
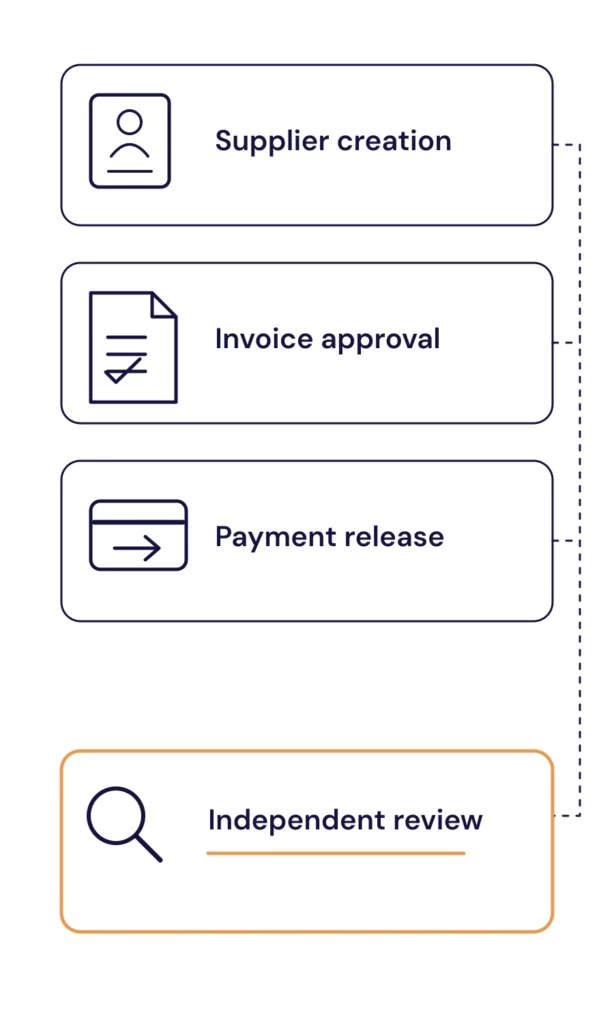
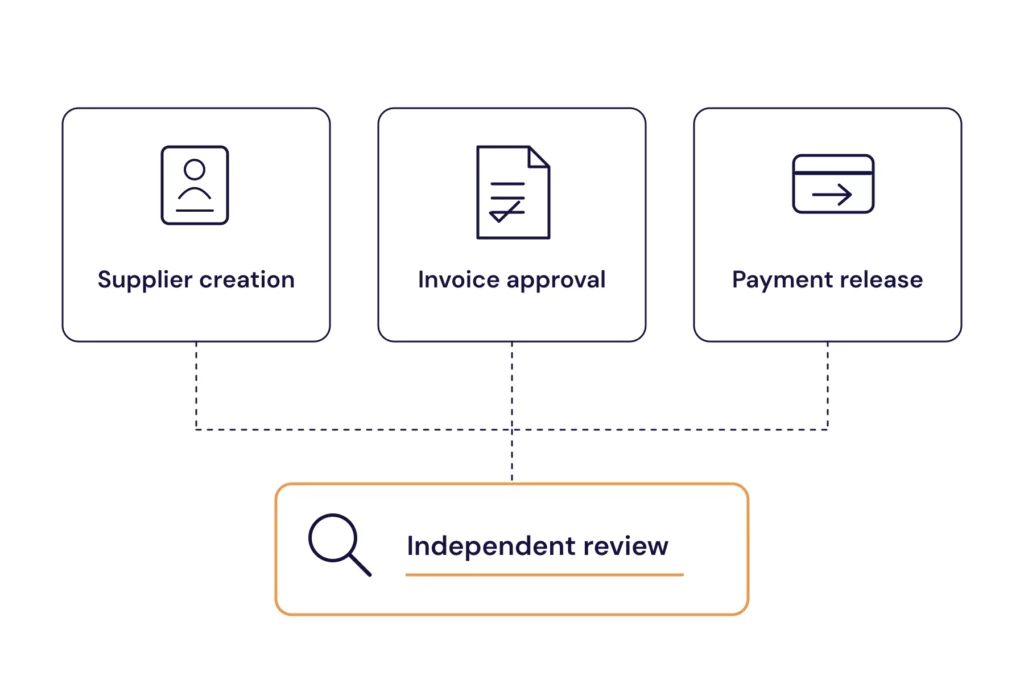
It is best to focus on the most exposed processes: procurement, payroll and cash management. Simple, regular and up-to-date checks help reduce opportunities for fraud. Some companies also take out dedicated fraud insurance.
VOS QUESTIONS
FAQ - Frequently asked questions about internal fraud
Before contacting us, you may have some questions. Here are straightforward answers from our senior consultants.
—
What should a business do in the first hours after suspected fraud?
Preserve relevant records and system logs, assess whether payments or access need to be restricted, and limit information to authorised people. Appoint a competent, impartial lead and check applicable reporting deadlines. Keep a record of decisions and preserve data when restricting access.
Is there a typical employee fraudster?
No reliable personal profile establishes who will commit fraud. Focus on access rights, approval powers, conflicts of interest and opportunities to override controls. Behavioural observations need objective verification.
How should you respond to suspected internal fraud?
Confidentiality must be maintained and premature accusations avoided. The company should secure relevant documents and IT logs, restrict access to sensitive systems where necessary, and entrust the investigation to authorised individuals. The investigation must be proportionate, impartial, documented and compliant with employment law and data protection requirements.
What sanctions can an employee face for internal fraud?
Established misconduct can lead to disciplinary action, including dismissal where justified under national employment law. Civil recovery and criminal proceedings may also be possible. The outcome depends on the evidence, the offence and the required procedures.
What is the difference between an error, an irregularity and fraud?
An error is unintentional. An irregularity is a breach of a rule, procedure or obligation and may be intentional or accidental. Fraud involves deliberate deception to obtain an improper benefit or cause harm. The precise legal classification depends on the applicable law and facts.
Must a company report every suspected fraud to the authorities?
Not automatically. The company must assess national law, sector-specific rules and any contractual obligations. A voluntary criminal complaint may also be appropriate. Suspicious transaction reporting duties apply to businesses and professionals within the relevant anti-money laundering regime.
Should an anonymous fraud report be investigated?
Assess its specificity, credibility and verifiability rather than dismissing it because the reporter is unidentified. National law determines whether anonymous reports must be accepted and followed up. A secure two-way anonymous channel can support clarification while preserving identity.
Who should investigate suspected internal fraud?
An authorised internal team, an external specialist or a combination of both may conduct the investigation. Investigators need relevant skills, independence from the allegations and clear authority. Legal, compliance, HR, IT and audit roles should be coordinated without compromising impartiality.
Can an employer read an employee’s work emails?
Access may be permissible, but it is not unrestricted. National employment and privacy rules, internal policies, employee information requirements and the GDPR must be considered. Material identified as personal may attract additional protection. Obtain jurisdiction-specific advice before accessing sensitive content.
Which EU businesses need an internal whistleblowing channel?
The general private-sector threshold is 50 workers, subject to national implementation and sector-specific exceptions. Some smaller entities are covered. A group-level hotline should not be assumed to satisfy every subsidiary’s obligations without checking the relevant rules.